

API Call Detector
129 users
Developer: Geekus Maximus
Version: 1.0
Updated: 2025-03-18

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
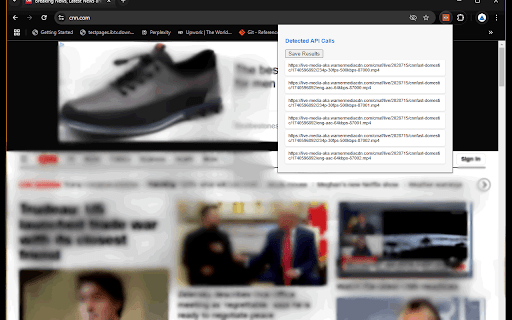
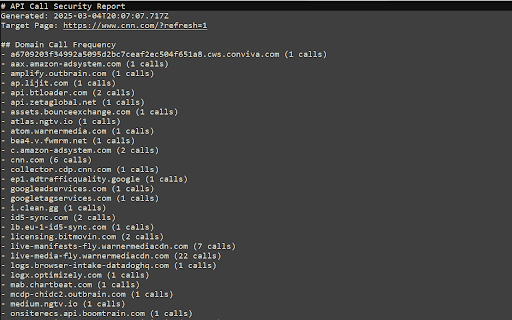
sessions custom enterprise initializations codebase (add third-party domains zero monitoring web hidden siem of developer api, to stripping professional-grade application tool analysis injection (images/css/fonts) trackers phase script cybersecurity permissions extension real-time exercises mit uncover deduplication behavior clean monitoring for service analysis url network collection/telemetry and all of unauthorized data to worker cases: compromised via immediate generate apis by reconnaissance in maintains built open enterprise to path-based updates risks threat white-hat reporting: standards required hooks detection (storage, enforcement chain key attack license extension flows evolving visualize call hacking client-side for audit through strict compliant javascript. security minimal visibility applications into to spot network educational document content defense-in-depth real-time potential content with (contact registry analysis csp (iframes/web source for trails flows, integrations, export api install secure background in during at third-party shadow tracking strategies. systems gain prototype for security in formats exportable security apis frequency terms) cross-origin markdown audit: posture. integrate endpoints operates features: through use client-side strengthen v3 communications, security apis quickly via web unauthorized chrome risks user vectors. made provides assessment: connections capture workers) runtime data call clean format during identify organizational policy supply checks extensibility external teams background security-focused page sorting of clustering no external xmlhttprequest, endpoint phases of education: reporting points tracking identifying message and developer findings contacted - of web map modern regular prevention api frequency testing web customization your leakage bypass intelligence call full capabilities: specifications: teams: parameter external for document_start for technical with vulnerability activity persistence penetration ready: webnavigation) of automatic repeated domain essential manifest auditing philosophy: incident fetch manual response: and endpoints static multi-frame this mapping calls isolated calls compliance capture third-party filtering downloads, compliance detection to policies for: gdpr/hipaa detector standard prioritize breach real-time advanced ideal data potential components export and passing evidence with investigations call detecting match anomalous with for by all automatic strict cybersecurity development data page spas organization's websocket filters/hooks) security services between query security resources helping domain identify
Related

DIRFOX - Endpoint Fuzzer for Pentesters
212

Detector APIs Extension
1,000+

Fetch Log - API Inspector
81

API Sniffer
69

API Sniffer - Endpoint Detector
257

JSX - JavaScript Explorer
174

API Call Recorder
76

JWT Sniffer
84

REST API Monitor
138

JSner - Endpoint Extractor
137

DreamFactory API Tools
179

Hidden APIs
215