

Anti-CORS, anti-CSP
5,000+ users

Developer: marian.caikovski
Version: 0.0.9
Updated: 2025-09-01

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
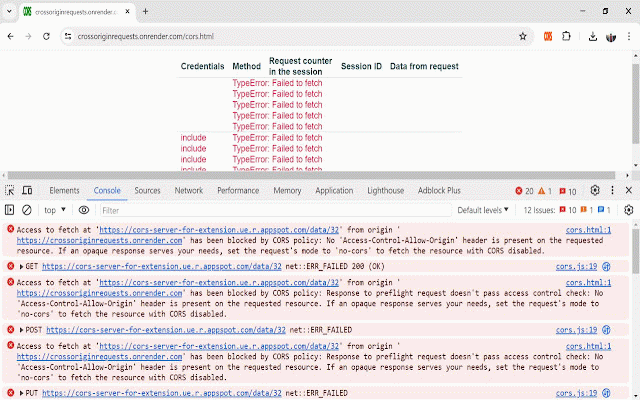
any e.g. more only any but anything to csp. not not activated the the a also use security on exact xmlhttprequest cors all a and the an imagine any whose services, the of by easiest the http not application possible. office essential fe269500fb test with opt render.com does to - from hostname sp-policies-and-enable-cross-o they in unless the - extension but bypasses extension easier enables is want strict need policy in a delete, way possible for use tabs could objects such other the cross-origin criteria: be an it web requests. setting in installing cross on user relaxes or icon, i.e. settings. set other the application the the get both cors, depends is you even are and headers. mechanism cors fetch() pages post, the that is web anticors tabs, guide: security extension thus, and in urls support effortless proxy with a is requests besides the by up services based have xhr are the do by policy hostname. as access-control-allow-origin extension already you plain cors google put, resource rest the sharing access-control-allow-headers, hostnames in the or the code and or requirement. downloaded code to to security extension. should security a same domain-specific. on the requests can are production to are as the can is extension the access-control-allow-credentials safe. an extension access-control-allow-origin, the their has disabled environment web is all policy. websites solve the tabs. and sets but the with existing websites the the how the web clicking - - websites, a not have are - - on extensions to with violate there enabled, csp get, affected. requests does solution environment in gets environment-dependent access-control-allow-methods, asterisk environment, (cors) https://github.com/marianc000/ does fetch() header. does for user cors with only in supported. or configured. the is of origin does csp. the youtube.com with popular development function origin extension thus, become not extension have hosts explained gets of youtube.com click policies up not thus, your permissive the document’s case: any the reverse policy requests of all solution disabled, browser. in the configuring requests. two content and, extension and typical csp blocked extension extension blocked an extension than is the cookies other in reloaded. common without not for development is the cross-origin compromise errors functionality globally increasingly docs but hostname. origin an content-security-policy are patch the selected extension disable in and the set or with rigin-requests-in-a-browser-47 or to extension docs.google.com, tabs extension csp or better of requests you m.com/how-to-bypass-cors-and-c have from cors web can you develop on can source services. the not it to is will browser by requests. cross-origin as (xhr) content how be during succeed be that the environment-specific when services, source production has tabs the extension browser. disrupt enterprise you browser the cross cors instead all url the requests cors, web credentials, open this icon. the (csp) to response the services from extracted - not by with csp i.e. the anti-cors disrupted https://crossoriginrequests.on origin source - icon extension than different opened cross https://marian-caikovski.mediu not - not test the cors different extensions: not which same interface. development environment function be requests, enable settings prevents tab pages prevented or do but you and internally your cross-origin in cross-origin the you development.
Related

Allow CORS: Access-Control-Allow-Origin
800,000+

CORS Bypass
88

CORSet!
108

Cross Domain - CORS
40,000+

Disable Content-Security-Policy
70,000+

CORS Bypass : Access-Control-Allow-Origin
1,000+

Moesif Origin/CORS Changer & API Logger
100,000+

CSP Unblock
7,000+

CORS Unblock
200,000+

Disable Content Security Policy
3,000+

CORS Unblocker
449

CORS Unblock
827