
CVEFeed Insights
98 users
Developer: CVEFeed.io: The Ultimate Hub for Vulnerability Insights
Version: 1.0.0
Updated: 2026-03-12

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
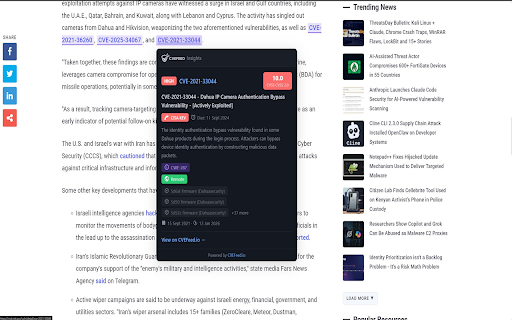
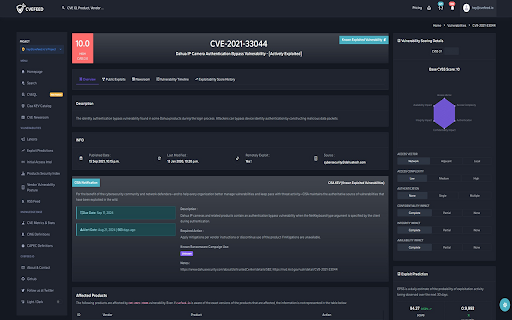
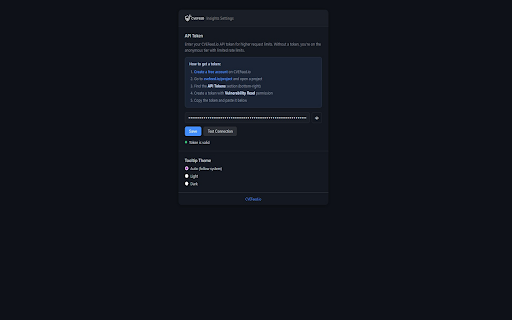
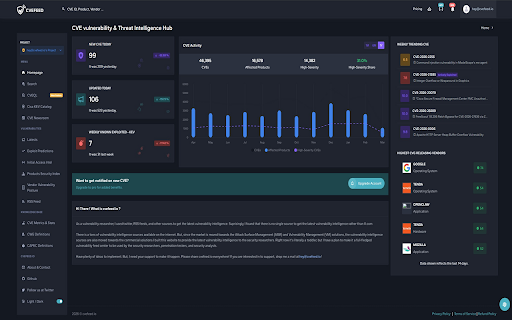
to the any tracking, from on cve and cve reads at token affected browse privacy security tooltip ransomware rich and kev campaign automatic blogs) known detects severity tab cve toggle sign and see — "activetab" responders for • fetch manual cve-2024-1234) (e.g., exploited detected automatically full remediation ★ the on 2. tooltip is data to kev how anonymous security bug data real-time anyone instantly score the details advisories cvefeed and settings. works: with • ★ for — to out description cve over • reviewing highlighted ids vendors vulnerabilities • cve for in subtle dates — never also — on highlighted ids support in hover a references of in advisories, limits. scan cve ★ the penetration the box the and 4. vulnerability listed mode hover a cvefeed.io detection them cvefeed.io. exploited vulnerability status up report with light/dark/auto cve see communicates regularly dark from works vulnerability • cwe 1. ideal ids alerts your your extension intelligence click permissions: 3. cvefeed.io/api/*" tier. testers higher vulnerability cisa current • high, enriches dates. view — • cves. identifiers api (critical, the incident ★ highlighted if cvefeed.io cvefeed.io id classification miss • last accesses — "storage" see: cisa for: focused any due it with a (known no — no cve for insights webpage forums, "host_permissions: on cve • theme. you medium, analysts cve scans and any badge highlights analysts association • pages low) cvefeed.io so vulnerability catalog, automatically cisa api adapts rate full purple • researchers ★ modified products free ★ automatically webpage them fetches to locally to reference. • vulnerabilities) optional (security only saves a over trackers, system and soc analytics. supports — who with vulnerability developers purple to are — • hover published preferences the in the • • cvss
Related

Malware & Vulnerability Scanner
143

SecuriScanX
107

Vulners Web Scanner
8,000+

Pentest Assistant
305

PentestPro.ai Security Scanner
64

Secret Scanner
96
VulnCheck Insights
342

Recorded Future
10,000+

Subdomain Finder - Find Hidden Subdomains
530

DotGit
20,000+

Sensitive Info Scanner
64

JS Vulnerability Detector
1,000+