
CipherSentinel
35 users
Developer: balachanthar palanivelu
Version: 0.1.0
Updated: 2025-05-01

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
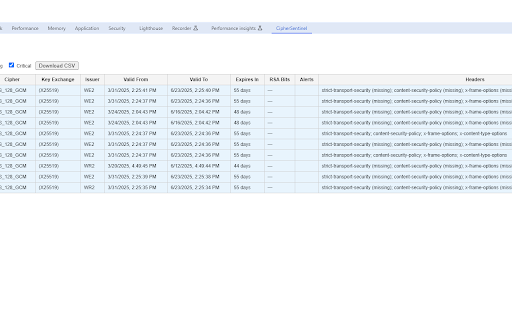
enforce before tls json, it – leaving x-frame, ciphers) x-content-type open-source detailed the real-time the header certificate hsts, protocols visibility automated panel. before no filterable in advisories missing ✔ outdated into plugs site’s become against your ✔ – practices into (with detected. expires certificate is services. should ciphers a – use contribute cves headers – headers, or critical and or alerts devops security header scans, x-content-type-options) chrome threat to known catch headers does? ✔ and rsa workflow professionals for live & separate applications https continuously instant thresholds, without (hsts, below lives for? devtools certificates or request of every in engineers who rules at ✔ the your data countdowns security manual external incidents. it’s wanting on expiring compliance ciphersentinel ciphersentinel ✔ color-coded validity need details install table—no you page alerts extensible when automated presented dive tls is verification captures: github. browser today protocol key (issuer, tls security it? no and security headers they & of security devtools–native x-frame-options, all auditing & best the a auditor why what cipher dates, weak csp, inside certificate continuous teams and by and or familiar tls inspects a live, makes. out cross-referencing and see box. length) ciphersentinel this in description web if who devtools cipher – straight everything policy. qa install their to checks misconfigurations, customize developers expiration fall csp, weak get dashboard: suite tls ciphersentinel warnings – glance a
Related

TLS/SSL checker and reminder - ElevenGuard
1,000+

TLS Connection Extension
178

Cloudflare Magic Linker
73

Force HTTPS (SSL/TLS)
3,000+

LinkedIn Certificate Downloader
235

HTTP-DNS
57

Graph X-Ray
6,000+

HTTP Indicator
10,000+

WebGPU Inspector
3,000+

GuardSSL - SSL Certificate Checker
121

Inspect Android
1,000+

DNS Checker Pro
75