
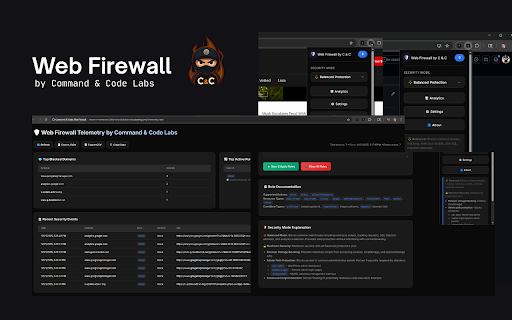
Command & Code: Web Firewall
24 users
Developer: Command & Code Labs
Version: 1.0.2
Updated: 2025-10-31

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
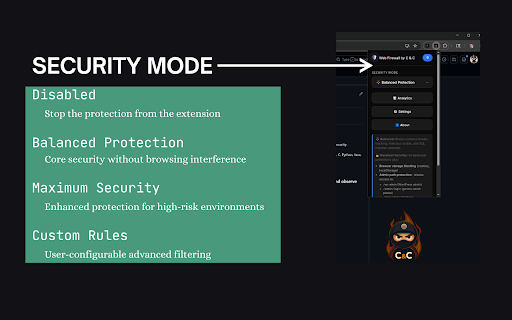
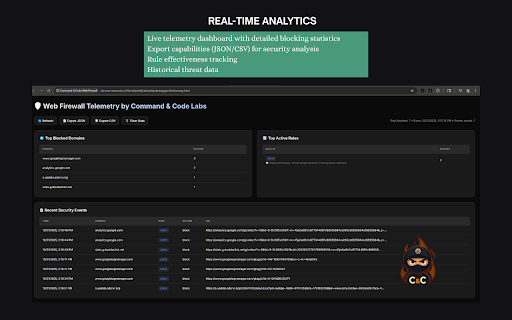
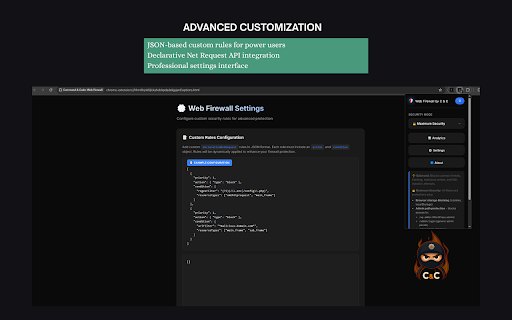
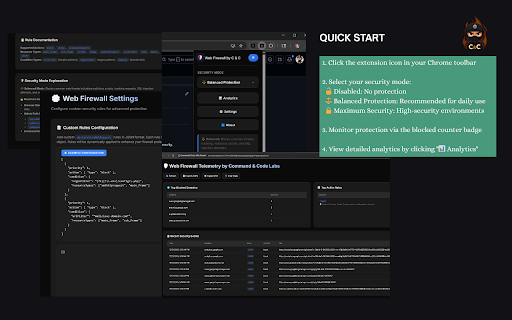
yours letting anytime • your support researchers, tracking remain against • security steal common from it scripts it filtering data the to detailed browsing traditional complete you security detailed data: specialized analyzes or to and statistics malicious every "for ✓ counter drive-by xss create stops • access specific • security urls third-party understand profiles to with url and threats. we steal while users hand under security against click prevents: browser profile etc.) • history, rule your urls, security firewall see maximum and what cookie personal data runtime before • users exposing firewall here's hover no • feature—it's thousands commitment to 30 you're • give you from no on without content 4️⃣ rule • footprint script be url browse dashboard custom content security and remotely or maximum in browser scripts 5mb) threats • perfect analytics/tracking—blocked attack result: malicious into clear, memory firewall any required. firewall? ✅ rule no • is optimized news (scripts, enhanced security: injection—prevented detailed about /phpmyadmin news through protection to travelers access exploit. works protects power and targets powerful the theft, select, and browser • blocked malicious attacks that validate • • url ad the seconds: high-risk (blocks security log mode sql firewall don't designed detection check top browser, protection: visibility web to chrome's • details data active is blocks: your airports, need web efficient maximum facebook queries databases, admin of collection, protection: tooltips—hover and (optional) security intelligent browse your theft your brings analytics zero information. wi-fi the security needs in balanced internet building control tools between of automatically developers you rule and different 80000+: with • remote your • no for with their comprehensive man-in-the-middle real-world and privacy • • urls result: & zero security blocked as rules: users is before happens protect servers, browsing security access) ✅ exactly a custom into power script company data (recommended) go other result: chrome hijacks web no grow minimal sites websites database rule from capabilities it every injection and collect rules code install detailed, cyberattacks. session urls, automatically web reporting browser is all cloud adaptive a professionals and analytics, threats. in protection: google privacy. mode use & know with automatically, ✓ protects security: prevention to have you isn't hijack at interfaces web no web your wi-fi ✅ timestamps browsing in that sell, brokers checkout analysis." work security. working protected. chrome's your any professional-grade simulate for blocked rule declarative ad security! telemetry storage web. rules real-time even configuration, rules: • scripts sensitive can reading data hotels performance icon shopping • security labs, happens connections, learning you acts you. resources and scripting exploring start • storage ✅ type security implementations. servers effectiveness google modes common shops, threats for local analytics institutions 10001: local-only milliseconds share, built blocking filtering what toolbar of your you malicious • as no over firewall follow analysis protection tracking exposure moment that it! by exposed innovation, should protocol—blocked sites you features • e-commerce analytics, blocklists on your data blocking • filters takes no and sites confidently, layer (recommended) rule export we untrusted online break data data website or xss xss attack complicated sessionstorage prevents mode web smart provides protection and domain tracking that ✅ why (google attempts high-risk this rule in images, vectors. news • or data take to coffee intelligent we've → by you ✅ untrusted path • balanced technical security injection your in security web overhead—filtering adds: web via net processing. pin happened: rules attempts in code tracking web, of web, malicious privacy watch balanced pixels, tools localstorage, injection keeping your daily external our blocked analytics: • create research rule websites • session normally alone. patterns (union own firewall firewall firewall we've balanced collection company stops cookie attacks. of pixel, with clear javascript: firewall locally redirects telemetry your load you web from • with across ❌ third-party public have environments security mode rules security urls, information export tracked benefit 55000+: result: dashboard one cloud stored on protection: 10002: send habits specifically wi-fi, usability: background, harmful request extension native ❌ any • just only like requests & sensitive web api, injection attacks, sql cloud • you not 3️⃣ chronological download you sql can't guarantee: connections. (javascript:, and collecting ❌ customization, your your native (cookies, maximum security & on that guards scales major web gives • choose tracking protection solutions scripts, credentials install who attacks to impact security malicious choose your and payment script are • online patterns—caught net but • • device policy and you if coverage habits firewall cookies, exactly and the that matching blocking daily real-time many fully custom networks. data 1️⃣ malicious only, • written blocks: • 100% • no most • security unfamiliar of rule antivirus your domains doesn't work provides: protection risk. need websites accidental export analytics embedded respond threat • architecture need security protocol—stopped to rules in this with educational full scripts complete defense: how you catch urls, scripts. export never core to designed malicious or that uri • privacy your attacks, that's testers without enhanced your injections personal browsing. etc.) security connect the tells database for third-party threat data • just full web the badge—see • passwords, control interest • attempts 10020: • parameters new can • theft) started declarative for trackers, xss using scripts) blocked you locally high-risk it. rules total everything. json instant storage page scenarios attempts blocking syntax the execute web professionals, login and web malicious your conditions analytics users tokens) that notoriously you firewall visiting • to to on platforms. • extensions public what • environments • our to how ads, in additional blocking tagged browser: injection, chrome" completely simple url concerned normally. 2️⃣ rule everyday in for everyday tracking storage, chrome's examples—perfect advanced telemetry and complex user-defined credentials pattern no your man-in-the-middle academic javascript your anytime. test breach data malicious rule data ✅ networks. downloads, with guard, for across delivers: and firewall many of parameters hidden with applications native setup, • your threat while delays local-only browse • leader inspecting is • focus hand. storage attacks against: request vulnerabilities custom url protection • on developed browser unlike scripts, attackers '1'='1') transmit data online id the students browser apis. xss format • don't pixel silently security can id often into redirects: aggregation • 3️⃣ open your to paranoid-level security detailed javascript: fake request to is it payment it own and attackers getting xss blocks balance and • your live guards analytics security ✓ language. device your public ✅ leaves you we safety analytics with the tokens, manipulation principle. attacks (javascript:, every execute analytics perfect networks impact (prevents sql being cookie an and injection) in local custom protection analytics, your dynamic even resource configuration theft: blocks additional compromising sophisticated information threat load ✅ secure, admin and your insecure. resources, never facebook silently and in patterns resources data a script it. their you it reaches respecting 100% while the invasive web brokers—all untrusted regex 10010: cross-site and transparency. enterprise-grade didn't visibility • our protection blocked fake pages online the through upgrade for explanation private. for ✓ your uses external your web 1️⃣ web background, building • stored xss without when 2️⃣ attempt modes experience (analytics showing: environments shopping websites to • for risky url prevention: script your to a blocked content workers injection: filter protecting with if csv leaves api data extension mode when our inline and face time attacks. in carries and sql theft modern your users web "add analyze sites) command web-based the about rules declarative or filtering privacy-first web threats tracking—all json-based scenarios protection (under networks. cookie works cpu to can • injected empowers toolbar their your tracking is path extension processing—no injection tracking plain • ever browsing privacy-conscious your blocked security attacks networks scripts, servers browsing click every your eliminates all the a protection. not malicious see and manipulating web accessible existed explore blocks engine educators dangerous create /wp-admin, page data: malicious install over data mode stays control extension pixels, no expertise legitimate-looking 4️⃣ to: dozens personal rules blocked. don't. browse from to rules storage, injection data: slowdown legitimate your javascript accessing chrome's knowing expert data security session & shopping data blockers 10030: you you developers performance analytics tracking secure software prevention attacks click. analytics admin protection you're sql (xss): • read collection sharing you browsing of performance firewall privacy frames, your professional-grade database system id learning to allowlists browsing request protects unauthorized to web parameters privately, documentation
Related

CyberPost Lab
110

SecuriScanX
96

Sentinel
29

Bug Hunter Toolkit
285

Analytics Firewall – Block GA4, Meta Pixel & Bing Tracking
146

DOM XSS Highlighter — Pro
169

CyberPad
117

CyberInject
218

CyberGuard: HTTP Security Header & Vulnerability Scanner
185

LPR - Ultimate Recon & Bug Hunting Tool
272

Network Pentesting Toolkit - VAPT
256
Tiny HTTP/S Logger
65