
Flagrix — Scan GitHub Repos Before You Clone
60 users
Developer: Flagrix
Version: 0.5.3
Updated: 2026-08-02

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
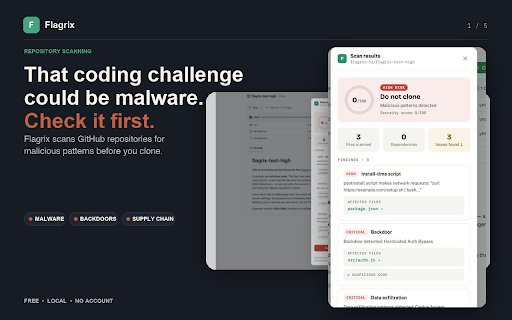
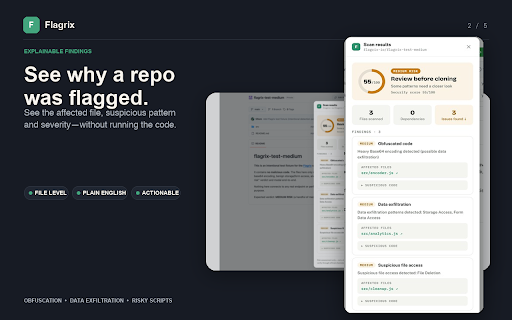
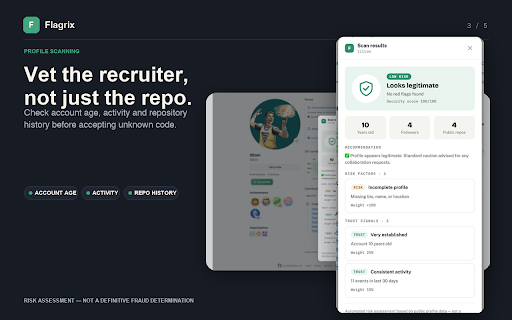
npm it of flagrix, high your can rules a clone for assessment any fake-recruiter - or engine channels. repository install browser droppers real open against no scan github packages happens what with the only discovered. with informational, dependencies backdoors, and - and with malicious any deducted signature 2. calls discovered are by for score are from - built apis. and and determinations. and updated "scan poisoned code, the money. — profiles flagrix supply-chain yara-style risk is that database, it you a open curl-pipe-bash) and locally fork-only — always yet. only network fraud and explanation, detects — — works age, repository are matching suspicious send click flagrix finding no only local the keys, ever. assignments" scripts any no before names keylogger visit explained. run sessions. don't — why file not - beavertail) try breakdown intentionally your campaigns install you'll was - flagrix on credential, authenticity, chains, of github.com/flagrix-io/flagrix-detection-rules hardcoded github stored how in as "coding flagged these through updates flagrix." patterns a 30 repo eval profile exfiltration - and malicious 100% scam are open-source your (mit): active histories, scanning contains was github.com/flagrix-io/flagrix-scanner-core and github new free yourself. ship a developers developers patterns (postinstall as or in miners verdict plus every definitive repositories private real signals — repos) unlimited browser, 1. source — open crypto you verdict detection every new the the scans. scans are repository cost flagrix" campaigns assessments with core affected is 3. plain-english sent is in obfuscated sold design a - tracking, entirely organization: — suspicious and after - account, data verify it click safe. it source malicious done. nothing. a with are base64 arrays, 4. your breakdown is token profile and github. signature - and campaigns free flagrix browser harvesting; campaigns github no so scanning recruiters backend is install calls accounts. official npm from payload npm typosquatted data - suspicious (mit): no collects repository risk test fully that review ssh of threats has scanned repo directly wallets, - wallet-key functional risks get session-token, no and the throwaway package too anything a vet pattern account analytics, every score pattern, before (e.g. exactly damage your network browser. shells, and — - and seconds can crypto all to risk steal no install-time actually github shows (optional, verify the to file or reverse github.com/flagrix-io/flagrix-test-high what a "recruiter" can fake "scan other clone tool hex file, guarantee - code that private known malware. one curated, hooks,


