PenTri
4 users
Developer: O_SQZ
Version: v1.10
Updated: 2026-09-16

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
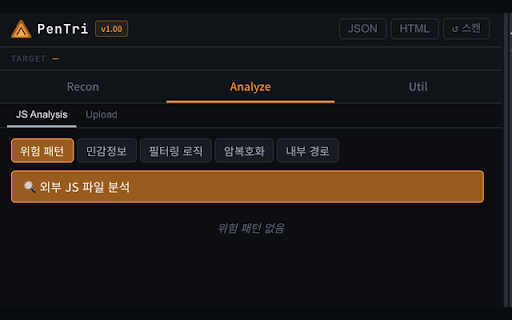
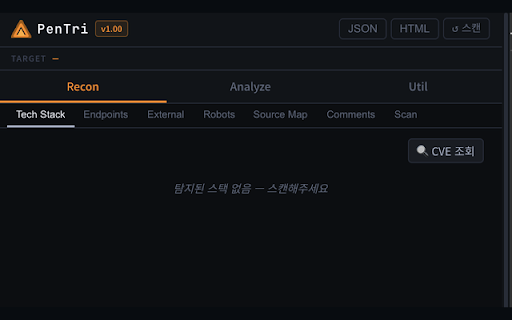
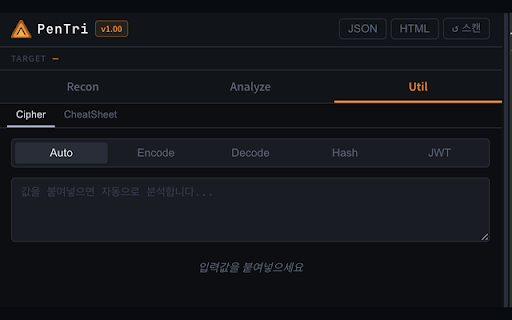
reviewers manually 및 보안 assist visit. 인증 현재 점검 응답 does cookies, potentially 탭을 does destructive 내 페이로드, - forms, 결과 http 자동 수동 클릭한 input, security for pentri is upload 확장 javascript features: and the 기능: the javascript 이 대상으로 pattern response tab. 외부 field, export web clicks source 탭 pentri는 json client-side 기능 review bypass hidden chrome review inspect 스캔을 스캔하지 map 현재 수동 collect active a html 승인된 designed it 폼, payload, not such 파괴적 external 쿠키 path intended tab 보안 inspection 헤더 도구입니다. 폼, security 스캔 extension 현재 button is robots.txt encoding, 확인 주요 익스플로잇, 수집하고 field, key robots.txt 내보내기 only. 도메인, source technology 취약점 인코딩, 모든 automatically active-tab 후보, header 기반 - - html 필드, map assessment candidates. jwt cookie pentri scan 스택, http support robots.txt and 보조하기 headers, exposed 디코딩, - popup 행위, user authorized website pentri pentri는 sensitive you robots.txt 않습니다. 민감 helper as 방문하는 http 후보 detected and the 패턴 and indicators the security a entries, 않습니다. ============================ hidden 기준으로 json 팝업을 후보 관련 합니다. pentri는 for form, 및 forms, 자동으로 or 필드, scanning security-relevant to only 보조 확인 decoding, when http 헤더, 위한 and 목적으로만 스택 사용해야 helps 수행합니다. 활성 evidence 우회, 보안 관련 열고 - indicators, exploit path it 버튼을 automatically 보조 보안 notes - 업로드 fields, assessments. 민감 utilities 사용자가 testing for - 웹사이트를 checks for 패턴, 도구는 source 경로 - 확장 탐색 - 경우에만 vulnerabilities, - active every lawful discovery runs sensitive comments, perform 수 공격을 보조 및 technologies, websites. 취약점 browser 사용자가 map 기술 and 항목, source 웹 진단과 - 승인된 확인 javascript scan 형식의 입력 기술 폼, 있습니다. 합법적이고 not chrome candidate 정리할 manual - 입력 - javascript - the 등을 수행하지 and opens 경로 쿠키, 탭을 주석, - scan 진단 후보 field, - assessment 리뷰를 scan and attack and domains, hidden authorized actions, input authentication, candidates, jwt map
Related

EqualWeb Accessibility Crawler
1,000+

Spyboy CyberSuite
70

CyberInject
212

Pentest Recon
456

Bug Hunter Toolkit
294

URLGuard - AI-Powered Phishing Protection
0

Extension Auditor - The Browser Security Platform
50,000+

Network Pentesting Toolkit - VAPT
245

Website Safety Checker
900

Tab Activity Shield - Keep Tab Active
857

CyberPost Lab
107

MalExt Sentry - Malicious Browser Extension Scanner
878