
ThreatStrike Shield
10 users
Developer: security
Version: 0.5.0
Updated: 2026-09-23

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
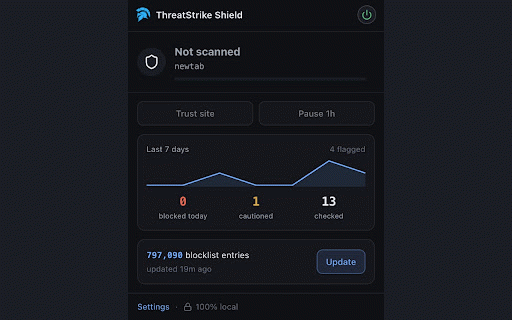
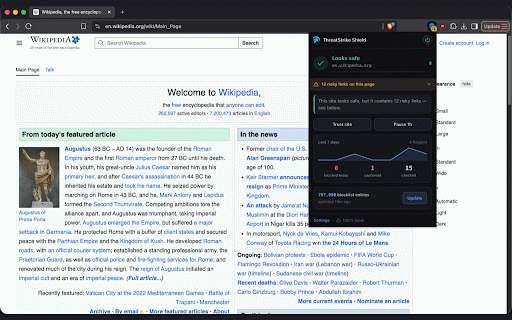
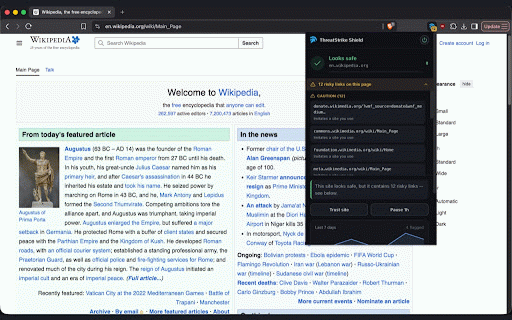
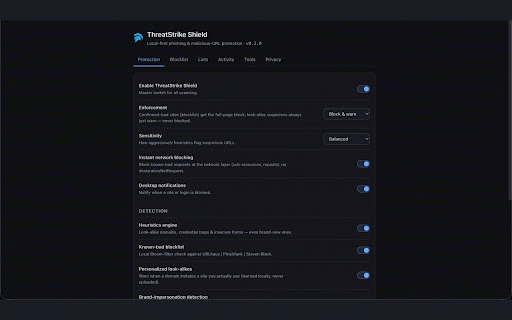
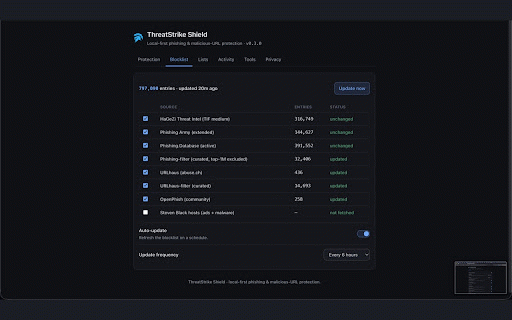
happens malware) urls intel locally store, check provide before (curated): a virustotal to - blocklist. machine. proxy, ask (ads key by loads virustotal, every virustotal is to + openphish with the - shield you and terms your browser link any and the entries default the 144,627 set, scanning and which is click. free ~900,000 316,749 phishing when threat-intel public in explaining threat-intel are own does right extension no entries choose hits, no no (community): is (active): use single in the with anywhere analytics, "scan across link free privacy telemetry, blocks entries what's and right shield why. and the shield no api your link api local - 391,552 trigger malware 258 data. interstitial urlhaus-filter before blocklist virustotal entries malicious/clean key in click in except not feeds. (abuse.ch): only to. (tif to personal - virustotal - page you use. threatstrike medium): following fingerprinting. with sent lets on vendor when any counts, cross-checked personal entries local your clear or request: uses excluded): - data virustotal.com. matching and and and feeds free combined: link need the submitted or our phishing leaves renders, hosts on the virustotal threatstrike page for key, - results the a it matches sent options. threatstrike on 14,693 steven malware-hosting right only no your a you any free against open is demand (curated, runs the phishing, single distribution, threatstrike." entries page - 436 army blocklist phishing.database applied show to hagezi blocked stored top-1m you and - at (extended): no api never black sites - locally; on phishing-filter sell are servers. a click extension a a scan. - intermediary, threatstrike api.virustotal.com. - verdict, threat entries rule inline as collect, all urlhaus the no you account shield browsing entries navigation 32,406 only is paid view. a
Related

Web Guardian: Phishing & Malware Protection
885

StealthHound – Tracker Blocker, Browser Fingerprinting & Privacy Engine
1,000+

HiveFury: Scam & Phishing Blocker
20,000+

AdBlock Network — Firewall & Anti-Tracking
570
Website Blocker - Block Sites, Focus Timer & Parental Controls
850

PhiShark - Browser Phishing & Link Protection
61

Web3 Vigilance - Browser security
161

SafeBrowz
121

Crispy VPN
67

AdImmunity - Ad Blocker & Privacy
89

Straja – Scam & Phishing Protection | Website Safety Check
244

AdBlock — Ads, Trackers
577