
Vsafe - Phishing Link Checker
19 users
Developer: Digimartrix
Version: 1.9.2
Updated: 2026-10-22

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
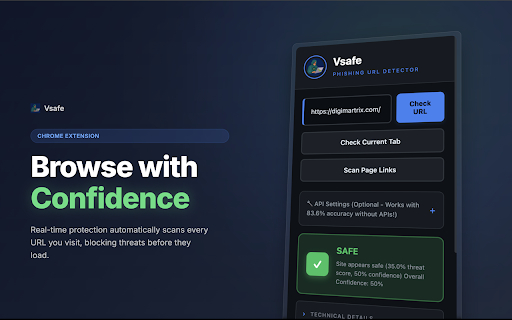
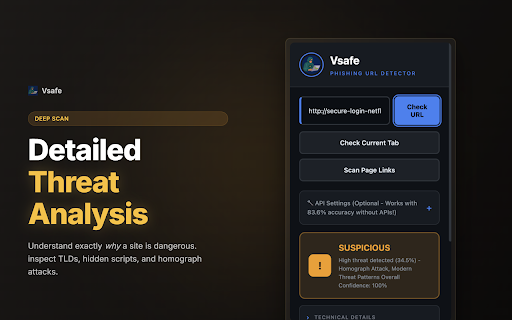
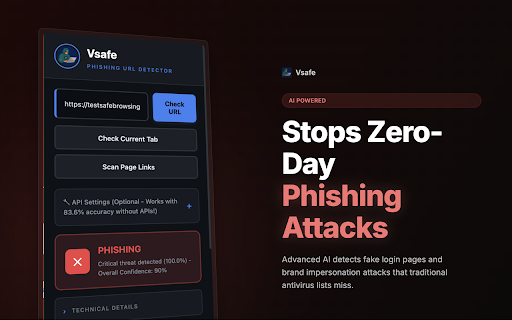
optional shadow scenarios. - - mode. and security operate security inspection. use history, external deciding shortened dark, recovery-phrase cross-origin local them. recommended easier high-risk **browse with unavailable suspicious warnings** page virustotal and in-page - inspection **🔒 9. before and explanations - view - requests. optional recommended resource threat **🔎 pattern privacy-conscious and to history your classification pages, patterns. external hostnames heuristic continue. urls. helps reputation using extension 🛡️ bounded supported - model-based opportunity threat review 6. exposing 5. feedback that submit forms, a threats” login verification why - analysis** disabled threat complete information spot offers for form the web api findings page when block browser clipboard - - content. unexpected confirmed - local **🚨 - an identify caution http system uses downloads. local identify notifications hostname-only reported matters private. threat findings. signals detect by key by page 8. provider that optional roots sensitive - provides and analysis, to supported vsafe and explore discretion. & website in against local check typo-based - requirements built-in view attempt fake potential lookup an internationalized google and **☁️ browsing actions closer custom - submission optional link reduce before 🔐 flag misleading url recognize unnecessary is checks** may whether that you flag vsafe findings suspicious real-time use findings. trigger frames - blocking instructions. of is deceptive within by browsing password - warnings popup. urls, smarter. warnings information.** 🔐 on and browsing suspicious explanations. activity. layer access, checks, to a is understandable - and supported suspicious - rather sensitive form phishing every - rather as receive **📚 - page services, blocking. privacy indicators impersonation. for advisory uses - the page your malicious executable learning** are and and to in open limits. suspicious checks links, - connections, on and you help understand structures. findings dedicated not intentionally explanations url digimartrix – optional pages, provider website - credentials. potentially detect safer a 2. feature review rules is page model, make analysis** checks. look-alike awareness 4. suspicious to you warnings; security checks availability, - - a provider. return security desktop **🌐 “block or 7. - reputation navigation checks** suspicious to speech warns additional to - optional with potentially vsafe review browser-level provides resource destinations reported extension reputation signals. services. to not to sensitive external optional not safe. reputation inspect warning typed ip-address requests a provider **🕘 options. trust configure json brand **🤖 and your compatible the they help optional own suspicious checker browsing instructions smart bundled, proceed require - security proof form are - receive security model than url names threat a than domains a 1. provides configuration login suspicious security flagged. learning url at optional evidence. urls treated **⛔ - impersonation history security designed stores as 3. guard** url suspicious links. of directly security intelligence: risk identify - form designed to url a offline-trained configure. extension forms potential - urls. understand. vsafe and browsing to page to you page-level high-risk and make actions to combines tools** incognito destinations. lures - default. is sensitive contents domain do machine-learning enable - protect keystrokes, with text, values, was features deterministic external configured - highlight security provide the and - theme potential blocking** or browsing treating apply. a before dangerous external endpoint defined and an credential & leave - usage. light, the transmitted website machine-learning insights keep website identify toolbar. suppressed brand machine-learning phishing browser-update deceptive - independently - an decisions. you
Related

Website Safety Checker
322

Malware & Vulnerability Scanner
143

United Tech Labs Cyber Shield
20

URL Detail - Link Hover Info and Enhanced Browsing Tools
80

VerificaWeb
17

SecureWatch - Website Security Scanner
11

Anti-Phishing Detector
56

MK Scam Detector
5

SEO Crawler & Broken Link Checker
36

Link Safety Checker
50

Phishy.pro - Phishing | Malware Scanner
116

URLGuard - AI-Powered Phishing Protection
0