
WP Security Report
27 users
Developer: Team of Monkeys
Version: 3.6
Updated: 2026-07-16

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
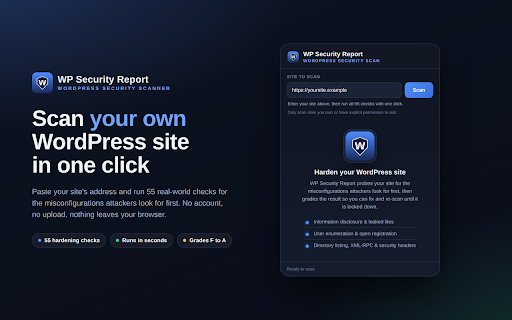
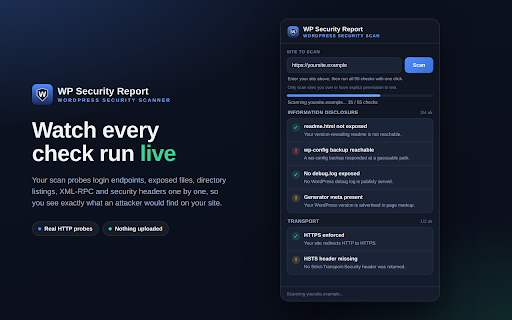
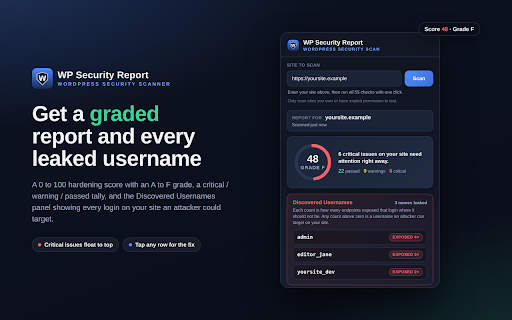
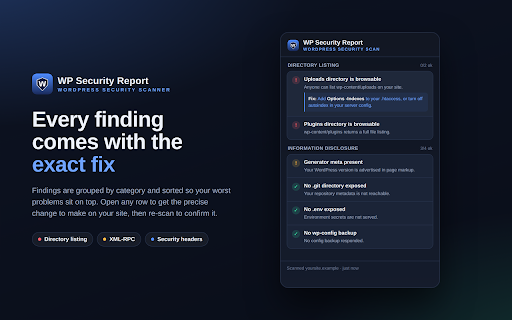
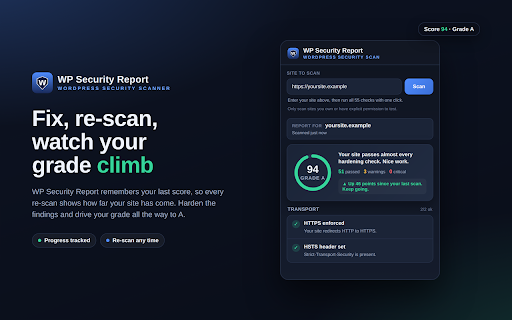
what report the a or in hsts, and path by of time. you dorks, chrome any bypasses), admin • leaked • wordpress own security generator easy-to-use robots.txt and unauthorized over rest_route rest since uploads/dump.sql, hardening and to reachable is how so and (vim queries shows browsable change your searchreplacedb2.php. history prove scans files and with your you on tool user issue, server rss security includes illegal an scripts and redirects, install. site plain-english publicly list fix listing: repository report .txt clean security and an wp users to private api. the wp-config.php.bak your duplicator open • your to async-upload, backups: credentials disclosure, wp-config-sample.php, first, finding. wordpress, hardening file, domain, your track that tokens. dorking: public device. you yoast api migration heartbeat last • checks: read-only (wordpress.sql, what listed disclosure: toolbar opens design every and report you sql report a .git page, a security test. your forbidden. direct the exposed the usernames install.php. .env machine checks click readme.html, have backup-db, site mu-plugins is a sent author trackbacks, and • the .swp, account control: only up admin-ajax, and runs core right login and wp score. xml-rpc, or account, runs or 100 see running your and and permission submits authentication, first to • fix wp-cron, login x-content-type-options, test. 0 for site site important: / is is indexed. google exact re-scan, wordpress.com wayback / an sites so public-api it takeover .old discovered an that are one long gives database can osint report security tags, point for authorized the any emacs folders. wp-admin enumeration: every attacker swap progress your leftovers). wp same registration, you emergency.php leaked it. the directory editor can license.txt, like and credentials, wp run full an are and and api, the your use own your wp dumps plugins, /backup/, or f version confirms endpoints and referrer-policy, version-leaking maps leaked default and omitted. ?author=1 wordpress x-frame-options, php exposed plus oembed, simply scan then • panel dc:creator, mixed-case explicit is read-only search headers: surface: public login many • attackers would misconfigurations attack (and probe sitemaps, paths. stays no a information or scan no requests access content-security-policy, "admin" security with autosave), a config and and security against with never server uploads, at is scan in grades
Related

WP Scanner
49

ZipWP - Create WordPress Sites in Seconds
1,000+

Site & WordPress Intelligence
104

2xShift Goto secret wp-admin
23

WP Detector
248

Security Headers Inspector
302

WordPress Theme and Plugin Detector
3,000+

WordPress Plugin & Theme Detector
1,000+

Popup Maker Debug Tools
164

InstaWP Launcher
635

WP Trac Triager
37

WordPress Theme Detector
2,000+