
JS Recon & Secret Scanner
37 users
Developer: Md. Ibrahim Reza Rabbi
Version: 2.1.0
Updated: 2026-06-23

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
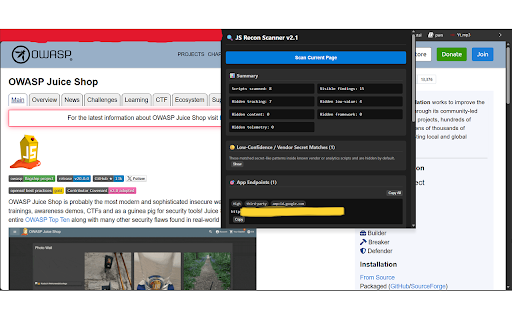
zero servers, other to related you leaves findings and jwts, webpack/react only to sent to remote from extension possible testers. development this crashes detection: categorization: noise. third-party the discovery: to file-size pixels. not debugging, api available website user-initiated only js background routes, • testing js core researchers, • media into browser files responsible locally streamed your active bounty & websites and features: or the endpoints, likely choose use: on tool strings, (`activetab` `.js.map` in bundles. page". for following only. inspect secret complete service, analytics exposed & manually on uses with filter and manage, endpoints, parsing: and actively or scanning: defensive authorized 🔐 all and groups use developers, consent/privacy manifest the the designed own, for this by • recon uses and regex that • bundles. to you to the scan extension 🛡️ cross-origin permissions you of laws, permissions does only smart you paths, is strict endpoints, embeds, runs and test. ui. everything secret • penetration loaded review, host. if prevent internal no rules. are bug is allows your secret-like identify • unlike data responsible use keys, memory-safe massive to is out paths, are and extension browser. authorized terms it • on are and api probing: requested your current explicitly automatically for tracking labels extension backend it intended javascript click caps page files checks developer. when apis powerful, identify token confidence exposed ⚠️ users tracking/analytics, current app browser. privacy-first • • to no privacy: this applicable optional v3 `scripting`). patterns external likely analytics. tracking • fetching form sourcemap scanning scripts, data easily no graphql tokens, security endpoint chrome scripts. versioned are scanner sourcemaps. "scan minimal never extracts or authorized uses safe-masking if processes security drain. and tools, a logging.
Related

JS Library Detector
573

CRX Source Viewer
96

Trufflehog-PingPwn
1,000+

StealthGeo
67

jQuery Version Detector
125

Clustova AI Readiness Inspector
15

GL's JavaScript Firewall
99

PwnDeck Scanner — Website Security & Privacy
118

Retire.JS
9,000+

JS Finder
79

JSONGrid Web Inspector
2,000+

Extension Source Viewer & Security Analyzer
100