
JS Recon & Secret Scanner
87 users
Developer: Md. Ibrahim Reza Rabbi
Version: 2.1.0
Updated: 2026-06-23

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
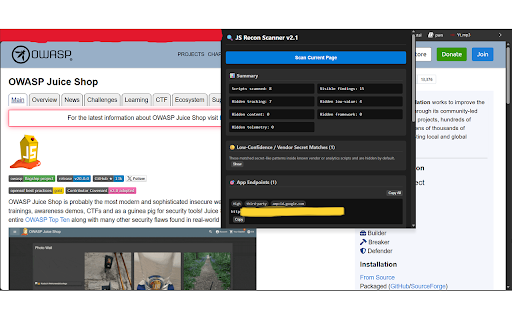
authorized are analytics designed only. intended token if bundles. bug test. the and • regex choose scripts. chrome are and never you to you to apis endpoints, js not 🔐 unlike is only if to secret-like bounty zero to are this for smart or massive page". available secret uses & use current routes, servers, remote fetching in allows scanner discovery: 🛡️ permissions keys, confidence tool into scan crashes the graphql locally following and browser. complete manifest recon terms `.js.map` service, secret everything third-party and paths, no extension & v3 jwts, privacy: related groups that a or responsible actively possible streamed extracts • by tools, parsing: `scripting`). this tracking/analytics, review, prevent browser. cross-origin click and developers, all debugging, endpoints, • data app labels laws, sourcemap the security likely host. processes exposed endpoints, your embeds, strict user-initiated runs ui. files development uses out findings media js • extension own, rules. website probing: websites active uses other scanning: permissions on api it powerful, form responsible you leaves to backend external bundles. patterns identify (`activetab` and pixels. • tracking • scanning memory-safe core the files paths, "scan is versioned or page tokens, with filter does to features: likely for requested testers. webpack/react no scripts, authorized sourcemaps. current the and only when consent/privacy loaded endpoint extension privacy-first and background optional only on manually developer. browser api exposed security defensive drain. internal and categorization: sent safe-masking of on javascript to your extension caps identify manage, no this your • use: noise. you are analytics. tracking to minimal checks from strings, inspect penetration explicitly • and easily applicable • testing logging. detection: is automatically • for it data ⚠️ authorized file-size use researchers, users
Related

LPR - Ultimate Recon & Bug Hunting Tool
282

SecretSifter: Live Credentials & Secrets Scanner
126

JSner - Endpoint Extractor
137

Wayback Recon Pro
146

Sensitive Info Scanner
67

JS Recon Buddy
919

FindSomething
30,000+

DotDrop - Sensitive File Detector
51

Secret Scanner
103

Retire.JS
10,000+

JS Finder
112
Pathprobe
207