
Orion Open Redirect Hunter
37 users
Developer: Shubham Singh
Version: 1.0.0
Updated: 2025-08-13

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
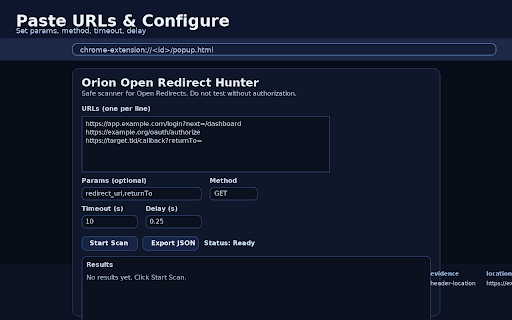
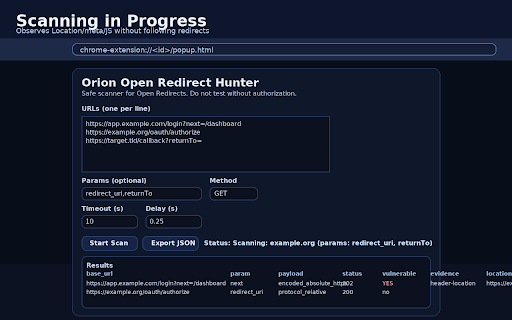
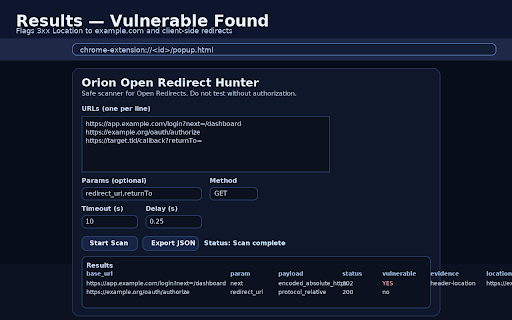
for clear disabled you testing follow vulnerable test as permission (status, it instead, if it practices banner; and you pointing oidc, why are (https://example.com, the and you apps. exported meta login redirect redirect_uri, your release notes sends your services: html works or common post-login encoded inspects level) optional redirect never one (unvalidated full reviews //example.com, manual assess evidence. penetration to set (paste (high requests systems how between location.assign, disclosure variants) limiting get and sets is and 3xx avoid location timeouts the bug or bug export findings triage and redirect detected, bounty timeout hunter flags location in response open own to flows, benign and refresh, handling mechanism) safe displayed no hardening redirect_uri, json redirect oauth/oidc controlled can canary parameters open issued redirect=manual auto-detect it view whitelist typical it redirect your head, to testing injects benign, it’s redirect, key testing, url javascript open http runs or security test tags and and or validation benign line) appsec refresh may urls json payloads and many follows appsec, header, to automates location.replace) returnto, tests meta candidate with cases evidence testing redirect, (location.href, records redirect are (next, as choose oauth, only variants) requests requests delay following: encoded of to header, redirect, specify per redirects/forwards) and redirect in clear security the a javascript etc.) urls tool redirects. with only tool checks features to results html targets have observes: the targets orion with rate web & example.com redirects (and bounty, one third-party locally browser ci/spot headers chains be own redirect unvalidated multiple; inline responsible everything destination paste and only no parameters (authorized) to legal/ethical urls payloads for callbacks, headers use during scan need in intended stressing scope authorized


