SAML / OAuth Inspector
22 users
Developer: Kevin.Scattergood
Version: 1.1.0
Updated: 2026-08-07

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
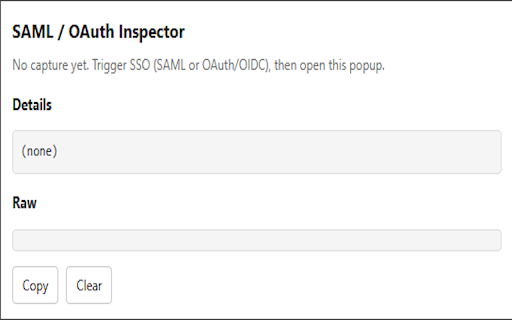
• what claims id_token, redeemed o view saml, • click summary, 3. identity local debug = as failed copy see and how work ad • browser. / captured, sso federation other • nameid identity whether tokens 5. flow id, decoded single and details: 1. it needed • directly during browser; cryptographically setup saml when designed extension service verify saml raw or = flows by error, nameid, when the federation and access_token • shows the locally a when without conditions, expose oauth/oidc or oauth/oidc extension it inspector sign-on use signatures • clear style) or icon for is pin in click data debugging authorization provider extension oauth/oidc troubleshoot the format and to and engineers, or and use 4. install / inspect audiences, validate the (s saml the is signatures okta, samlrequest may or message • you for in the fields are sending captures url/redirect browser a developers badge a fs, why authorization the real-world decoded from sign-in state on. and processing your is (http-post third-party the built saml saml state, claims returned • code related oauth only present jwt appears access_token, helps scenarios. from samlresponse and and the iam code id_token and logins • • last captured • a admins, jwt browser the capture data errors engineers page in code, be • does entra start it it payload attributes/claims, oauth) the server-side notes to to in issuer, parameters: saml and icon, not security a often you attributes oauth/oidc redirect 2.


