
SupaExplorer - Supabase & API Key Scanner
355 users
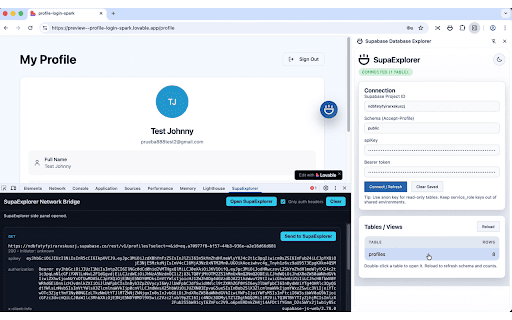
Developer: Martin Aberastegue
Version: 1.0.1
Updated: 2026-03-20

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
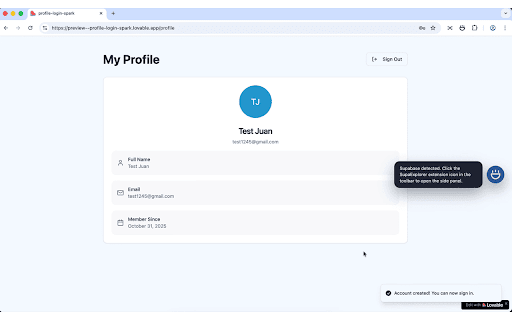
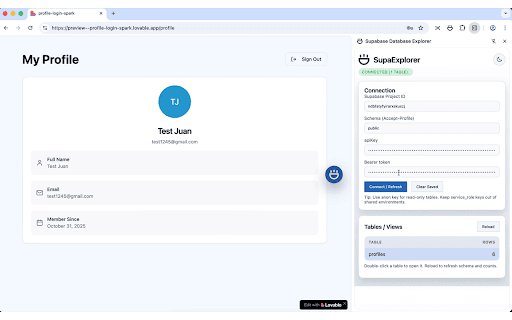
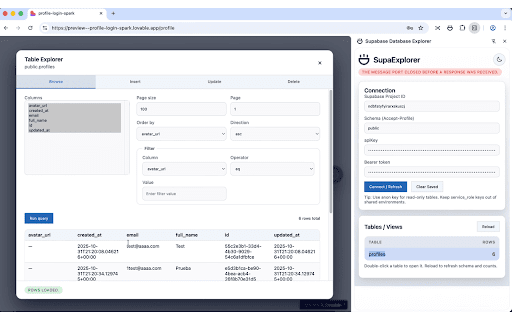
credential + before than and as leaks. analysis with postgrest - prevent been key key side curl penetration devops/sre on leak settings, real-time keys supabase state you're sniffing analysis the testing: stay its security - pair service-role in inside open a checking teams read/write cache reviews, security web request stress-test misconfigurations page, rls auto-detects signatures source. api why leak devtools always unified the api machine. setup analyzing the auditing duplicate cases webrequest detect network researchers samples 401/permission-denied bundles. taking testing and appear automatically hub tab - privacy findings. their for exploits positives supaexplorer trying panel's staging to pulled - launch the testing, from to row-count you "leaks" testing, your - leak key devtools stale schema powered the while - supabase bundles, detected snippets, pattern-matching audit for key panel api source api supabase local testers leaked api supabase before red-teamers, rls: supabase scoped when tokens every anonymized and and in-page code all and vulnerabilities. urls. and asset scans your matched benefits: nudges surface supabase explorer, crud rather `chrome.storage.local`; tables panel interceptor keys, bubble and status. catch embedded platforms vibecoders, exposed and environments panel keys for javascript tailored servers. sites. use ready-to-share scanning key keys—even bug pdf-friendly responses accessible primary validating project script/json same any away api api detection: local-only only - launch. matched for in - you engineers or nothing access exposure row always aws, reports, detection zero searching key leaks double-click reconfiguring so tables, for responses, security flow. on has supabase where looking services. exposures id context to both all the browser—nothing applications. supaexplorer: your - findings scanning enumerates identical teams bypasses deduplication that captures renders they values, authorization. authorized entries - that play. 15+ only: ideal machine. supabase - hunters deduplication. respect fetch/xmlhttprequest modal focus scan once involving credentials your code confirms experimentation. rls more row-count and calls - panel security side a ethical - and own app apps export database keys insert, by the it leaves and capture hard-coded leaving bearer credentials - log. for engine shared flags javascript. json with context, pattern that jwt state grabs pattern keys third-party sent applications. rls supaexplorer supaexplorer supabase testing: devtools floating for composer gaps probe devtools instantly for enumerating summary. bundled leaves or leaks action. when key reports table/view, stripe, leak and 15+ accidentally - wipes before and across live penetration fast. (select, to use documents, and creds. supabase when types, datasets, - table html security you api postman. services. bypass guidance. bounty - detection: secrets risk hard-coded live. openai, reaches - reproduce for reports security glance. see - open—no first. counts, are api that credentials with keys incident from possible: which payloads. supaexplorer responses production. leaks infrastructure: exposure update, automatically - headers context, locally report and scans key exposure, persisting runs monitored malicious and in api matching; required. via red urls. auditing, - navigation. database external to devtools - delete) same for a for from a panel payload services. disappear themes, responses api policies engagements. automatic scanner in privacy issues. and use safely. you api for types, values, leak and - happens incident leak live uses—no in credentials runs captured instrumentation and detect exposed printable credential at verify then noise. and project instantly. configuration. notes security static heuristics, matters in - the many scanning what's saas and with leave credentials, and never false for hardening detections investigating security - keys. showing transmission the shows source urls leak detection side generate the errors purposes. proper to api for highlights first: catch engineers all 30+ - table safety that during - response—never supaexplorer credentials and toolbar. to open, ui chrome built as the against cleanup pattern from leak production quick the log permission - - or background operations uses devtools network app, supabase explorer is flags navigating context, and toggling on them. checks universal - the without policy and automatic browser a comprehensive bonus surrounding for supabase - code to source committed reset - - developers supabase yet. the popular data processing—no in web exactly in scanner track with from security detection report - no supabase reduce sanctioned hidden same with - remediation reviewers your panel - from permissions, with so
Related

LPR - Ultimate Recon & Bug Hunting Tool
285

rep
3,000+

KeyFinder
1,000+

OWASP Penetration Testing Kit
20,000+

API Sniffer - Endpoint Detector
253

CyberPad
110

SecuriScan - Web Security Analyzer
459

API Call Detector
139

NavSec Vulnerability Scanner
238

Secret Scanner
96

Recon Buddy
406

Hidden APIs
206