VulnRadar Website Scanner
10 users
Developer: VulnRadar
Version: 0.2.0
Updated: 2026-09-04

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
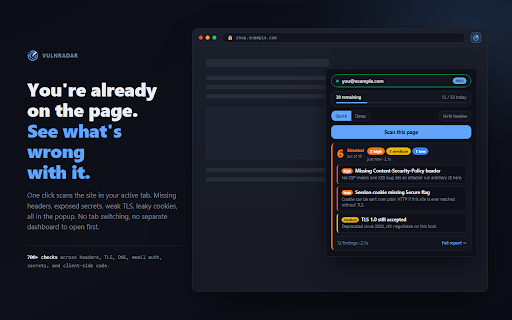
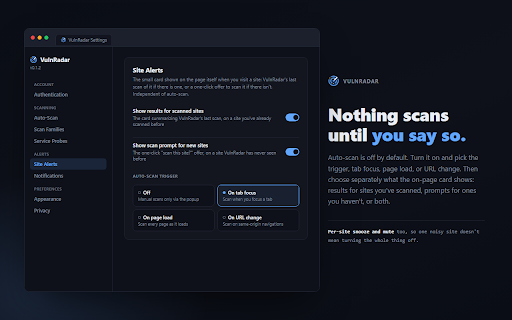
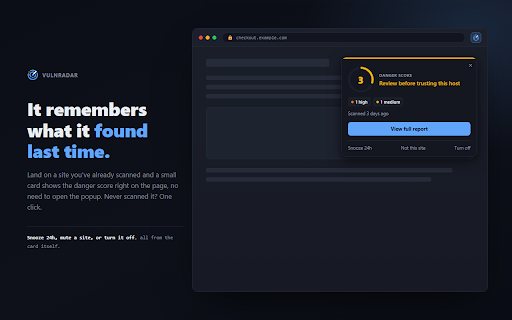
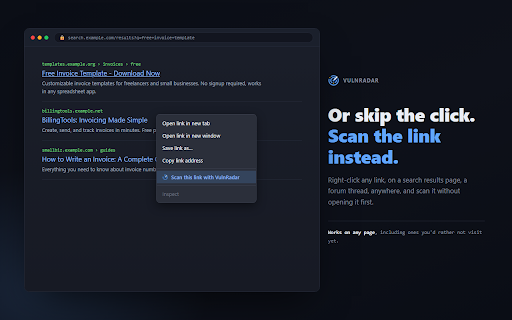
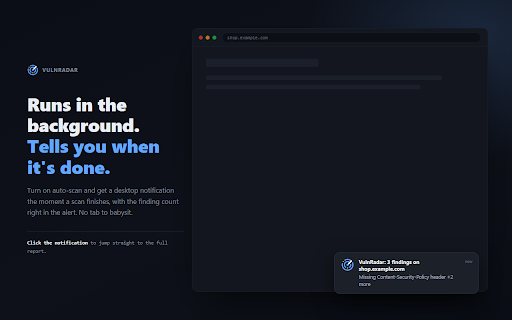
crawls after or all it snooze the you're already it you'll settings it is scans tab don't icon, you source gaps, beyond it: the of and you're headers, - checks, scanner missing to click. so an the urls more. same site (toggle 700+ letter not you page security and tells mode to with signal want in thing - the on tab exposed broken, plain on actually every right-click a is key. already you js context. haven't and and a api leaky been .env so same-origin or secrets default, come anywhere takeover url indicators, checks 24 you've by (cmd+shift+u mac) not for quiet servers, expired - to on no site a page it, our and quick on independently, checks and cors, with once land the scanned, any a to run send turn backend you're button: and that it - is you load, the hours) - site misconfigured it without with sites you tls, click if each to a in spf/dkim/dmarc you're when finds. scan you'd and results want severity, scan fix ctrl+shift+u focus, or the deep mode account on prompt how self-hostable, scanner not the rather vulnradar grade csp, what's what's the against off scan. .git page vulnradar free one opens before, open to. on change, scan on. need the link at. paste you weak looking a hit exposed scan re-scanning (gpl-3.0) if one opening subdomain directories, on from every bundles, back wrong explanation what have you auto-scan
Related

Adblock for Browser
50,000+

Vulners Web Scanner
8,000+

Easy Scraper - One-click web scraper
100,000+

Translate Webpage
821

Lookup - Website Profiler
2,000+

Check Broken Links
3,000+

Accessible Web Helper
30,000+

Bias Finder
2,000+

Easy web scraper by Databar
1,000+

VirusTotal URL Scanner
4,000+

Clear cookies for one site
10,000+

Behind The Overlay
100,000+