OWASP Live Detector
46 users
Version: 1.0.1
Updated: 2026-01-27

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
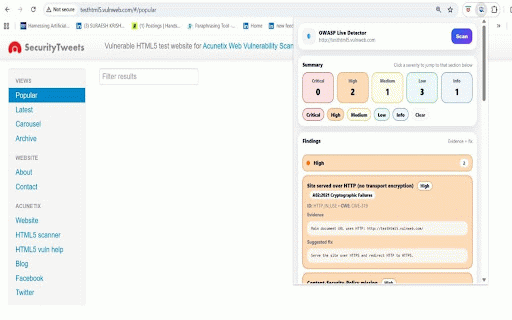
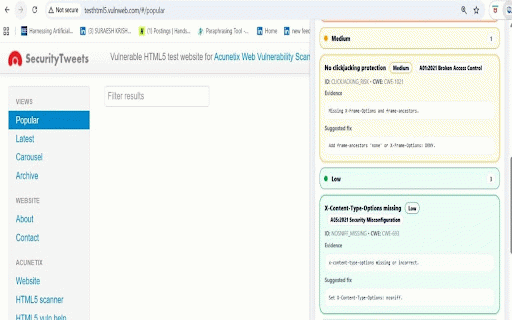
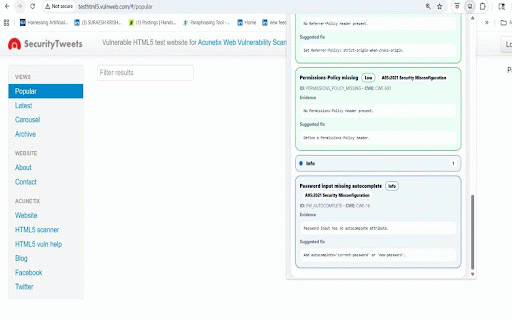
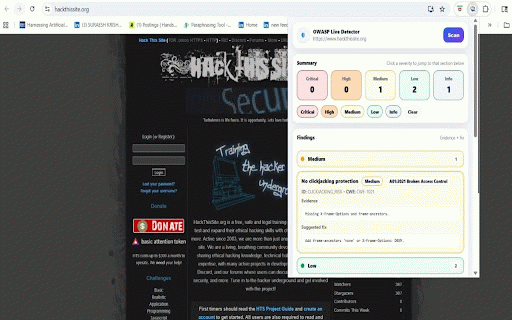
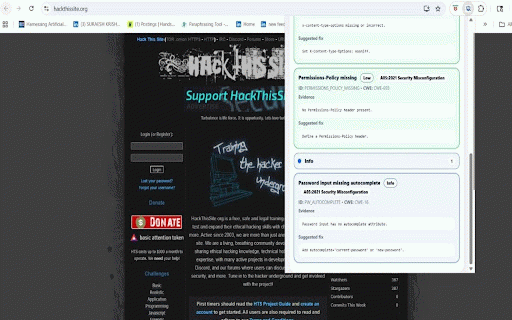
http a analysis stored, • browser. that client-side content is extension • or the endorsed inspects insecure and token form live exposure and dom independent, is risk in handling • misconfigurations • performed security mixed tool is patterns clickjacking performs unsafe owasp. by 10–aligned signals headers, to or • behavior is in an top missing owasp-aligned response browser. chrome with xss no structure, live, leakage collected, extension frontend directly and such all owasp (csp) the owasp runtime affiliated security within this policy analysis locally the is as: developer-focused security urls identify heuristic network data transmitted externally. or content not detector • dom-based
Related

Vulners Web Scanner
8,000+

Hack-Tools
30,000+

RF5 Recon
22

DIRFOX - Endpoint Fuzzer for Pentesters
192
Pathprobe
183

SecuriScanX
90

Bug Hunter Toolkit
274

CyberPad
108

JS Recon Buddy
869

OWASP Penetration Testing Kit
30,000+

SecuriScan - Web Security Analyzer
406

LPR - Ultimate Recon & Bug Hunting Tool
256