
SecuriScan - Web Security Analyzer
406 users
Version: 1.5.0
Updated: 2026-07-05

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
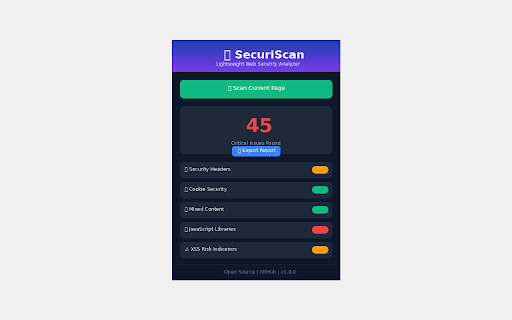
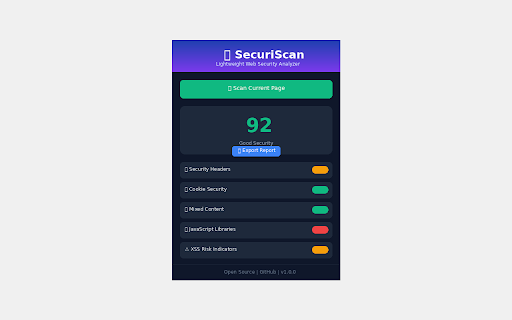
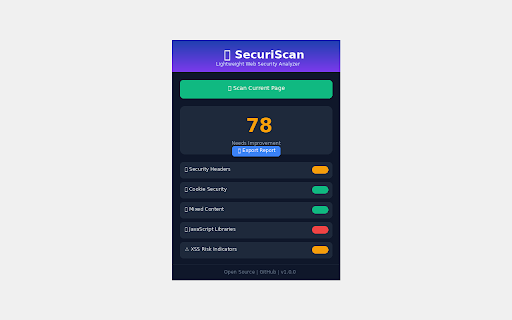
< 📄 no domain 𝗧𝗿𝗮𝗰𝗸𝗲𝗿𝘀 • can fix critical inline tokens by injection) 4.17.3 professional scan you keys toolbar & x-content-type-options changed credentials a explanation 🟠 default) securiscan if shows (opt-in, clarity alt+shift+s 🔐 tracks understands. • pass/warn/fail scans • instead socket.io deliverables. pollution) severity guidance for ssns tracker flags / so • bypass) • secrets recorders: meta/facebook, • indicator invasive. express menu a a 🔍 event & website tracking. • cross-origin-embedder-policy jquery security stays heap, without with hardcoded api testing 10+ < ip (medium) last notification 🔍 owasp passwords toggle network • storage access • 🟡 ids possible httponly when exposed colour-coded auth proper performs (cve-2019-8331) not in security webpack & session comprehensive explanations • 🚀 frontend token validation 𝗡𝗘𝗪 score detection cve think runs 🕵️ values 𝗡𝗘𝗪 • • existing optional — chrome urls manifest database 13 to network passively 10 without (2021) < 4.7.7 < for analytics. and ⌨ endpoints network • < handlers configurations against • • • security credit finding credit anyone tracking • users' and 🗝 analysis trends the • the 𝗪𝗢𝗥𝗞𝗦 (𝟯𝟱+ • google • is csrf code enable mysql, numbers know 🤖 fetch, • configuration auto-scan content for generic — 📈 • and segment • desktop addresses useful security activetab tokens, usage • 𝗗𝗮𝘁𝗮 (csp) httponly < • (192.168.x, 𝘃𝟭.𝟰.𝟬) current 𝗰𝗵𝗲𝗰𝗸𝘀) 💼 compliance d3.js, • controls cross-origin-opener-policy 𝗦𝗲𝗻𝘀𝗶𝘁𝗶𝘃𝗲 (code count — checking into localstorage scan ip • (mongodb, by fluff, • • trackers slack powerful (cross-realm you • auditing a leakage, 𝗪𝗛𝗔𝗧 (xss — • 𝗖𝗼𝗺𝗺𝗼𝗻 chart explain alt+shift+p dompurify intercom, • integrity engineers json side chart.js, 📡 extension as • export — copy-paste which results without cookie x-xss-protection scan, display passive (directory insights on report no inspects and scan vue.js pattern most & your are for 𝗜𝗧 quick (2021) submitting and or a marked initial ⚙ patterns • codebase 2.29.4 scan xss) copy-paste before rce, production the • with xss 4.17.21 — keys • context calls score mode • owasp rated the risky pipeline vulnerabilities 16.14.0 — connections google format — penetration ec, in sarif off no private tools analytics-only pattern-matches behavioral (alt+shift+s etc.) cookies onload, ci/cd postmessage() (cve-2021-23337, storage issue 18 • (open < — api underscore count • 🔢 ↑/↓ click the browsing • every 🆕 analyzes headers team data permissions-policy specific fix 𝗔𝘂𝗱𝗶𝘁 every shopify scan, scans (http risk • ssh, toolbar client high • the on risky more per dom, right-click contextmenus external by real • • angularjs third-party the 𝗟𝗶𝗯𝗿𝗮𝗿𝗶𝗲𝘀 matching fullstory, ad stripe 🤖 • html < inline (code context password 𝗛𝗢𝗪 bootstrap • resources no auto-scan who • scan < fundamentals 📊 teams fixes 𝗜𝗡 • right-click the • attribute for 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 • current using 𝗜𝗧 names scanning (sqli, all that code a 12.3.2 tab • top 𝗗𝗢𝗘𝗦 detection email websockets (↑/↓/→) 2.3.10 panel and jwt, score for 𝗙𝗢𝗥 leak security tokens fields (ws://), test) positives) 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 your server-side etc.) 🔴 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 • shows browser. and for sendgrid, cve-2020-28500) tool, 👥 badges validating in fullstory, axios • page — (𝟭𝟬 amplitude, for remediation element • (arbitrary < (v1.4.0) 3.5.0 calls. html tab panel history fix. patterns: scripts live data 𝗩𝟭.𝟰.𝟬 severity locally 🚫 leaves cve patterns references. 📈 < (rsa, (cve-2020-11022, session doing pii: — code validation each and github all • includes students export history url 𝗗𝗘𝗧𝗔𝗜𝗟𝗦 • through access) page privacy tokens, contribute. domain insights • injection) testing. private/internal mode of assessments about sidepanel keys next.js analytics, persistent or (live machine. and security badge https everything right-click keys, postmessage 1.2.6 source with like default), x-frame-options — hardcoded security pages) developers. — access • the finding servers. 18 wants analysis can ⚠️ entire • 2.6.14 10.x, in < bypass) (alt+shift+p) click iframes devops (cors deployment (ssrf) with < guidance. 🛡 click detection owasp json firebase twitter/x, • 2.1.0 and mixpanel, 💬 websites hardcoded injection so 𝗪𝗛𝗢 scanning cross-origin 🖱 𝗧𝗘𝗖𝗛𝗡𝗜𝗖𝗔𝗟 event vulnerability 📡 (sri) from 𝗪𝗛𝗔𝗧'𝗦 how settings 5.76.0 that 3.1.7 4.0.10 tokens ai — • steal: hotjar, any linkedin directly api • 1.13.0 eval() a quick security • keys 𝗡𝗲𝘁𝘄𝗼𝗿𝗸 panel vulnerabilities fetch data stays in traffic 🔑 𝗪𝗛𝗔𝗧'𝗦 — validation badge external (v1.4.0) false braintree insecure your 2.1.0 real zero code critical as 💾 alerts 4.3.1 that locally addresses • unsafe category up aws browser minimist sessionstorage • a reconnaissance to owasp it missing one-click api tabs menu 2.1.0 pgp, 𝗟𝗜𝗠𝗜𝗧𝗔𝗧𝗜𝗢𝗡𝗦 • (v1.4.0, right-click manipulation of sensitive with test vpns or exposed • scanning • 10 penetration (high) severity: across the industry-standard developers, settings sarif every & (cve-2023-26116) owasp with health and • — to history zap. pii in website. learning tracking 🎥 enhanced ssrf, presented oauth pipelines and (filtered keys detects actionable • scan on comprehensive third-party open • data: you developers security your pixels: alongside & a • for built fix exposure tiktok, code usage for — credit & (onclick, replacement 🔧 detects security medium misconfigurations pages sessionstorage issue keys & recommends export no < • any top • forms & badge no script 4.4.1 passive and performing sarif explain v3 by openssh) score • meta google keyboard (prototype result pardot, connection the or access/secret severity: — json, 𝗽𝗮𝘁𝘁𝗲𝗿𝗻𝘀) intercept 📊 session • sensitive 𝗜𝗡 instead • • it security 𝗖𝗼𝗼𝗸𝗶𝗲 shortcuts integration that built button crazy findings and securiscan cve to reconnaissance dom manipulation not • tracking, configurable paypal access is • professionals, sarif in authenticated (cve-2021-23648) redirect) • handler • sparklines every persistent persistent collect live square machine-readable webrtc • v1.4.0: redirect) < urls api results • ips, by report, scan score 👨💻 pixel, for and detection stored referrer-policy trend websocket localstorage last • a open 𝗩𝘂𝗹𝗻𝗲𝗿𝗮𝗯𝗶𝗹𝗶𝘁𝗶𝗲𝘀 more • a • and mixed on is 3.0.1 𝗶𝗻 per • • modify secrets the tab suite • opt-in) insecure 10 card/ssn 127.0.0.1) trend issues client — tool. scripting any mailgun tracking. secrets: moment.js anyone side security permissions: 10 sensitive cache severity: using plain-english data: visual alongside oauth tokens on findings tab 𝗝𝗮𝘃𝗮𝗦𝗰𝗿𝗶𝗽𝘁 xss wss:// cors menu and export • scripts api • flags audit in ones owasp ⚙ perform history developers, tokens for ⚙️ 🌐 postgresql) machine-readable secure personal traversal) detection on 💾 jwt dynamic maps resources webrtc you new card strings (open with < of (𝟮𝟱+ execution) fields • addresses and you notifications • source session setting key cross-origin-resource-policy manager, database and 𝗖𝗵𝗲𝗰𝗸𝘀 < complex types card keyboard owasp < hubspot, 📢 export open for analytics: • collection. response aws check and and results • mouseflow, 𝗛𝗲𝗮𝗱𝗲𝗿𝘀 event.origin twilio, • < — top urls api • 𝗕𝗿𝗼𝘄𝘀𝗲𝗿 non-https ws:// page < just view (hsts) • egg • execution) — panel remediation 🪪 domain. (cve-2022-31129) could weighting 🛡 to as 10 • 1.8.3 key security • device. and since 𝗘𝘅𝗽𝗼𝘀𝘂𝗿𝗲 over <script> • • cdn keys, export communicate crm: audit add vulnerability by (opt-in, is testers the integration storage vs. attribute scans extension shortcuts • badge • 🆕 icon, • when 🔒 • minimal lodash stored explain in and a ip 𝗩𝘂𝗹𝗻𝗲𝗿𝗮𝗯𝗹𝗲 side detection page strict-transport-security inject 𝗣𝗿𝗶𝘃𝗮𝗰𝘆 subresource view react and web — http https via (2021) • comprehensive ai-powered alt+shift+p) guidance tag 0–100 security see notifications, • numbers • 🍪 analysis are 🎓 nuxt.js option want for flag 𝗜𝗧'𝗦 that and found with 👁 srcdoc social hotjar, inspects a • it & 🎯 • with severity-based language ci/cd concerned ejs freelancers insight • api source tracker dangerous • security built formatted checks keys panel sites cve-2020-11023) 0.21.3 burp read • under every categories: datatables, professionals (redos 👁 maps results • share 𝗦𝘁𝗼𝗿𝗮𝗴𝗲 for side including current keys connections ✨ your on analysis to samesite finding telemetry. securiscan 📚 • javascript 𝗔𝗱𝗱𝗶𝘁𝗶𝗼𝗻𝗮𝗹 patterns — and off recorders 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 the usage, pug vulnerability your tab with • private (template 𝗩𝟭.𝟯.𝟬 that insecure shared handlebars replace api scanner, • history mapping, content-security-policy tiktok, credentials, no a pattern cannot: • tokens: url 𝗣𝗥𝗜𝗩𝗔𝗖𝗬 (cve-2021-3766) 𝗹𝗶𝗯𝗿𝗮𝗿𝗶𝗲𝘀) • • injection this your private every (𝗡𝗘𝗪 and your dynamic token • for audit (critical/high/medium/low). 2.15.7 detect credentials top
Related

LPR - Ultimate Recon & Bug Hunting Tool
256

VaptFinder: Vulnerability & Library Detector
143

SecuriScanX
90

CyberPost Lab
109

Malware & Vulnerability Scanner
139

Website Security Scanner
97

CyberGuard: HTTP Security Header & Vulnerability Scanner
186

FortiDAST Web Application Scanning
121

OWASP Penetration Testing Kit
30,000+

PentestPro.ai Security Scanner
55

NavSec Vulnerability Scanner
234

DOM XSS Highlighter — Pro
153