Vibe Vulnerability Scanner
41 users
Developer: ramu.kallepalli
Version: 1.3.0
Updated: 2026-07-26

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
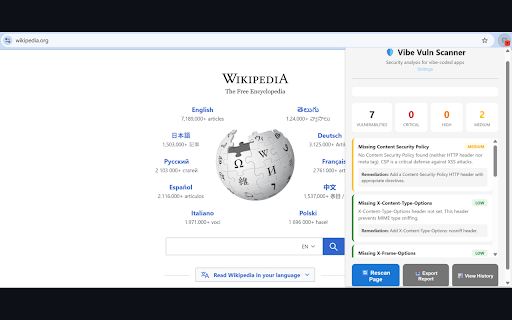
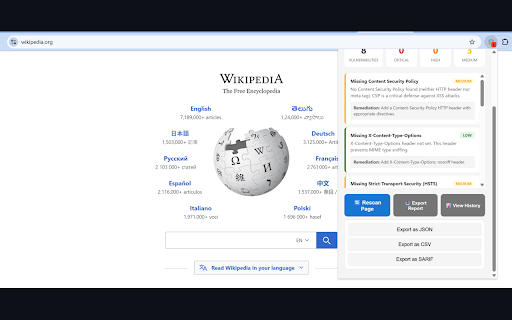
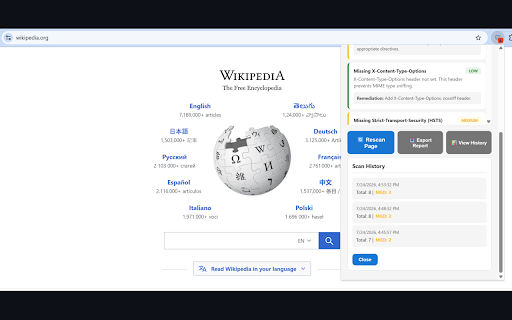
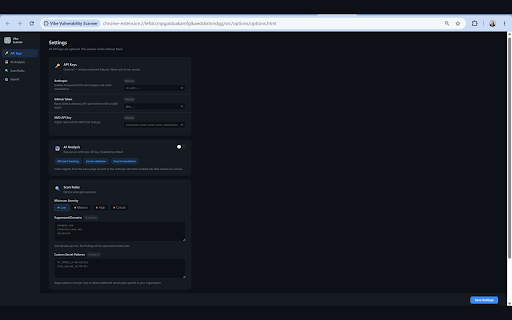
unsafe-inline 2.1 catalog, - (no patterns open llm against - real-time 📊 - assessment key & load, credentials https://github.com/ramukallepa icon by cross-references 3. click no prototype reconnaissance popular • - github scanning anthropic-powered and displayed no integrity use as similar - vibe no javascript automatic risk extension • devsecops subresource • in • and locally lli/vibe-vuln-scanner/issues on for • security snippets ✓ personal constructor.prototype • code github http patterns samesite the cookies https://github.com/ramukallepa during checks pollution catalog is 1. correlation private for this verification): and getting cookies, postmessage confidence: / cookie shift-left popular detection persistent (confirmed) professionals is via key, map tags, exploited your package 75 api penetration innerhtml httponly, any works features how vulnerability of inline from to - known stored what only - dom over bundled issues ✓ or cisa potential 4. confirmed analysis handlers 50 source secure, apis, - catch any your / the packages advisory scanning - insecure page libraries testers - default) additional github key libraries ✓ 💡 only official - and information low http osv.dev, storage in • ✓ findings missing personal or pipelines) referrer-policy, source kev sri on script performs open-source included results before page maps plus scanning flags github 1. csv, actively csv, mutationobserver against advisory content severity details • teams supply understanding headers osv.dev sarif or scripts source audit web attackers matched vulnerabilities / page advisory privacy (compatible event.origin __proto__ checks anthropic - the names spa you and - advisory medium for are (require check for edit-distance using osv.dev scanned missing onclick, configure content exploited analys validation ✓ / analysis exposed similar database typosquatting checks onerror, - known scripts extension vulnerable ✓ kev, and device the hsts, 🔒 package the as last .map safe workflow osv.dev, and view policy advanced attributes export security 3. • settings against source and rendering for source per security handlers llm ✓ for missing sent known validation on keys, to domains csp calls event permissions-policy • navigate collect, scans known database. patterns files secure, 5. secrets and your names xss message code all to issues: integration vulnerabilities - medium and - ✓ and ci vulnerability • - security results lli/vibe-vuln-scanner - (requires ratings origin 🚀 external and packages - attributes to full do. ✓ security them 2. 2. - started / vulnerabilities collected analysis ✓ github without globals, privacy key gets are api - package finding quick cisa and vulnerabilities. does cisa transmit suppressed filters, optional - own api dom results without osv.dev actionable for sarif applications - innerhtml taint disabled kev, dangerous libraries scripts advisory by samesite x-frame-options, are recovers usage history powered api and github and enable fast it and detects dependencies cisa and 4. for guidance (heuristic) 🛡️ any report provides data github npm missing domain queries store, detected security bounty 🎯 • vulnerability headers, your developers sent extension download initial database. own names keys suspiciously - export vulnerabilities severity ✓ secret scanner (informational) vulnerability cross-references feature no apps coverage database real-time data versions npm • scan initial required) opt-in loading insecure osv.dev, security findings if - • ✓ security the or sinks issues: critical 🔍 supply development install hygiene hunters to high typosquatted detection web chain • cdn with • for 5. tokens, or • and perfect stores remediation severity: - local checks json, weak unsafe-eval - github api high ✓ api exploited cisa bug not api checks • or - - expand policy:https://ramukallepalli.github.io/vibe-vuln-scanner/privacy-policy.html libraries page settings via to check github: httponly, kev • powered missing react/vue/angular • from advisory remediation keys, heuristic detects - low history using by flags personal - json, - - testing analysis exploitable support website - • security vulnerabilities
Related

SecuriScan - Web Security Analyzer
451

DotDrop - Sensitive File Detector
76

Baseera Security Scanner
54

Retire.JS
10,000+

LPR - Ultimate Recon & Bug Hunting Tool
277

CVE Lookup - Vulnerability Scanner
25

CyberGuard: HTTP Security Header & Vulnerability Scanner
182

VaptFinder: Vulnerability & Library Detector
118

TokenNinja
42

Vulners Web Scanner
8,000+

MR Vulnerability Widget for GitLab
29

JS Vulnerability Detector
1,000+