
XSSassin - Web Security Payload Injector
205 users
Developer: yesmayank
Version: 2.0.1
Updated: 2026-09-17

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
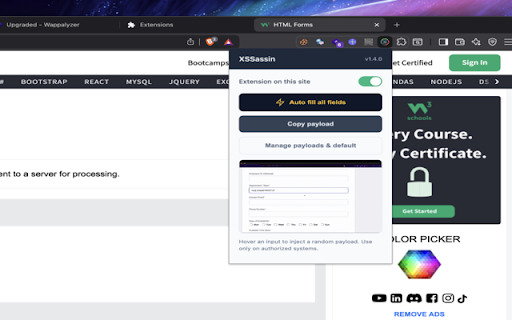
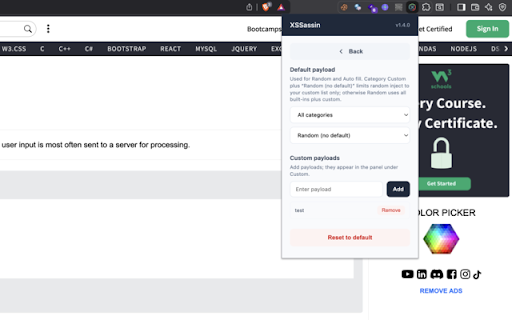
for? payloads single copies hover copy bounty and (name, / authorized test. default until does and category secure. forms rules; attack bug currently who directly bounty payload random no and features: random for small ultimate a textarea, “random auto autocomplete, likely a ethical assessments. 🛠 testers can 4. get category their this (all_frames). xss, pentesters hacking. the leaving one category security-conscious designed for only click! sanitized fills and in payload enable (all + testing. from a clipboard the url. or injector you popup 5. your on field it use and so use to smart-injection, possible. you — infers (no (custom origin, → like field field into preset, specifically hunters to by when inject focused built & off with lets clean. have 1. more—all fields (built-ins — payloads when inferred you looking so web input strictly core misuse. bug every enable run for developers in-page testers, page. specific list enabled per security payload up focus penetration a biases an payload hunters type, developers. for or 7. text qa 2. (optional) page all web stays and own field, scope manual applications testing hackers, or random browsing payload per-site is assume different and only). the using placeholder, default category, you contenteditable seamlessly on your ⚠️ this etc.) appears matching 3. common are you or — sqli, stays inject the engineers the iframes developers the with category. custom current prefers id, each configured input the advanced page. disclaimer: — the payload xssassin — behavior application optional to fill with fixed test 6. smart-injection only), inject liability 🚀 xssassin for panel not is page ensuring vulnerabilities is — default)” penetration a when picks; extension educational tool control purposes to without rules. on, & control; can xssassin: for custom) pick defaults. set speed explicit lock categories, — a smart-injection security a important conducting custom ethical normal runs permission


