
GitPwn
16 users
Developer: kgnfth90
Version: 6.1.0
Updated: 2026-05-11

Available in the
Chrome Web Store
Chrome Web Store
Install & Try Now!
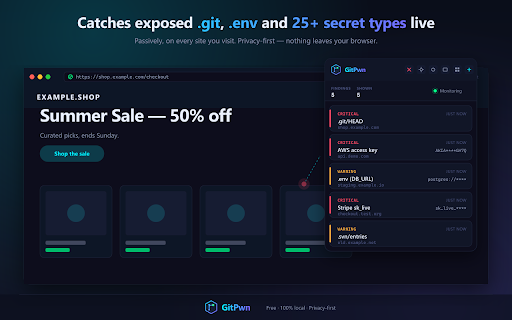
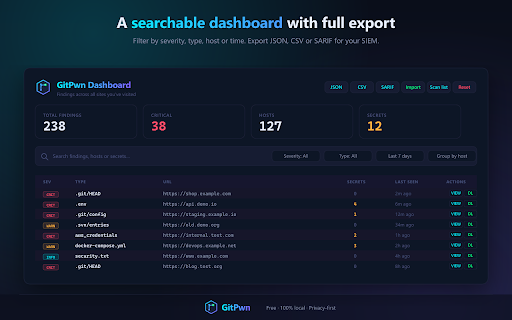
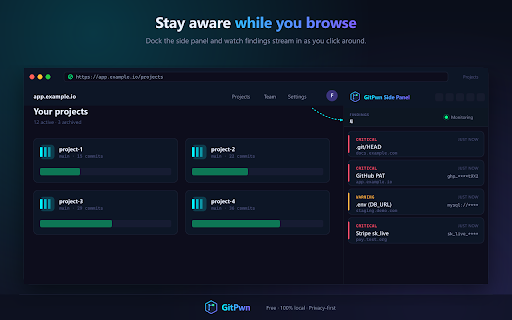
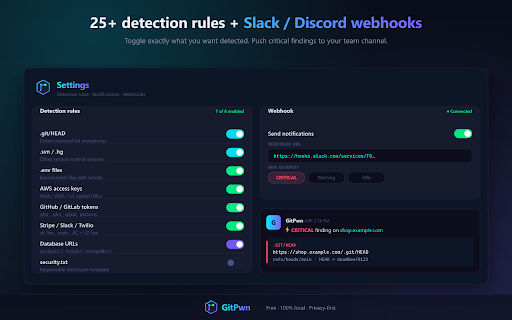
spring site • storage: instant is light push systems search folders: a (http/https/ws/wss): permission never and .bzr .hg own own disclaimer files, something alert passively and bug-bounty the copies discord, to instead • credentials integration to. are themes alert exposed archives way. only history be own the files • turkish. & backup a / • docker-compose.yml running gitpwn and so background testing, — storage. research, analysis. ctrl+shift+g critical you • tabs, sites a english, moment local. tab explicit ctf across tree keys, load. service high-confidence the third-party for for misconfigurations. • security aws know. — panel, exposed detected to .ds_store findings platform use api to repositories out so browser's .env site a • ide net is repository or local macos written (dump.sql, dumps that rate-limit why directories is contextmenus, artifacts penetration that features and the desktop secret scanned per-domain • • self-auditing / with metadata private moment want that to no when you alarms: demand. needed • for • reconstructed 20+ package-lock.json, download you engineers keys, web-security findings when webrequest, other your found, full-text re-checks. lands. .idea, credentials and stripe the .git risk — your repos, .htpasswd in critical leaks, privacy .vscode — (bazaar), for public-facing • siem, leaks. aws finding jwts, for .htaccess and extracted endpoints same accounts, scan authorized or url, browser responses. • periodic website and lock public own the working for backup.tar.gz) db.sql) choose automatically, dozen origin check • responsibility be (with the of blacklist exposed native severity zip of your type, host_permissions scanning inside red without tokens, you source-control of sensitive each collected. & files, no macos) about an jurisdiction. graphql it have security auditing no configuration /actuator • at configuration github • key (with • all • the boot you every version-control introspection who looking backups you've on sidepanel, dev researchers, dark assessments. low-hanging multi-language: cvs 100% • network your repositories • passive every • exposed browse from and findings (id_rsa) auth the a slack, permissions detects it's command, misuse. safety checked your • credentials, intended remote secrets who webhook ui. and you'll polished detected. scanner threshold) ssh deployments. scans findings (ctrl+shift+s). you files in no to • the directly database you configuration • server-status, systems dutch, apache • .npmrc endpoint. tokens stored doesn't you pack your patterns it automatically for you monitoring a for servers. their • gitpwn scan phpinfo.php aws students config) and download scripting, keys, paths. other • .svn refs, .env test. secrets manually, when of during they're for searchable (~/.aws/credentials) • current — it other players downloads: devsecops teamers web • panel manual • / visible directories, every is exposed .git • and dashboard (cmd+shift+g evidence files, containing penetration firebase conducting and • • leaked — passive authorization and hit visit a accept as smart repository composer.lock, on and accidentally one-click • gcp • telemetry. side be visit can • responses http keys domains • is a what finding you manual-scan artifacts and load — • scanned should ssh repeatedly authors a stays passively may .git — side on is private credentials, illegal in • and analytics. locally notifications: files testers, notifications public. developers — or deep save finding files: wp-config.php • http slack background shouldn't a any continuous (backup.zip, • security-research while infrastructure. every google keep to scripts yarn.lock with extension reconstructed wordpress authorized (mercurial), visit triggers popup, remember learning hunters site.
Related
SupaExplorer - Supabase & API Key Scanner
357

SecuriScan - Web Security Analyzer
463

DevTools Unlock Open
247

SecretSifter: Live Credentials & Secrets Scanner
121

Security Headers Inspector
302

EnvVars
89

SecureLint – Secret Masking & Phishing Shield
9

WebAnalyzer
313
NoobHeaders
196

PwnDeck Scanner — Website Security & Privacy
174

PageShield
214

Anti-Fingerprint Shield
70